In the ever-evolving Android threat landscape, robust application hardening is a non-negotiable. With adversaries continually refining their approaches to rooting, debugging, and tampering, a proactive, multi-layered security paradigm is imperative. This article delves into advanced mitigation strategies, including root access detection, anti-debugging mechanisms, and reverse engineering obfuscation. By embedding these practices into your development pipeline, you ensure your app remains resilient against even the most sophisticated attack vectors.
1. Root Detection: Mitigating Privilege Escalation
The RDHelper module encapsulates root detection mechanisms by abstracting key checks to identify rooted environments and mitigate privilege escalation.
Key Highlights:
- Root Access Verification: The RootChecker utility evaluates system-level integrity, employing RCResult as a sealed class to abstract rooted and non-rooted states.
private fun isDeviceRooted(): RCResult {
    return if (rc.isRooted) {
        RCResult.Rooted
    } else {
        RCResult.NotRooted
    }
}
Frida Detection: Employs library scans (/proc/self/maps) to pinpoint traces of dynamic instrumentation. Abstracted data fetch optimizes security without exposing implementation specifics.
private fun detectFrida(): Boolean {
    val suspiciousLibraries = ABC.getSuspiciousLibraries().split(",")
    val mapsFile = File(ABC.getMaps())
    if (mapsFile.exists()) {
        val content = mapsFile.readText()
        if (suspiciousLibraries.any { content.contains(it) }) return true
    }
    return false
}- SELinux Enforcement: Ensures SELinux remains in enforcing mode to curb permissive vulnerabilities.
- Root Management App Discovery: Identifies common root management packages via system-level package scans.
By combining these techniques, RDHelper reinforces device integrity detection with minimal false positives.
2. Anti-Debugging: Subverting Debugger Intrusion
The AdbManager abstraction orchestrates anti-debugging safeguards, encapsulating core monitoring operations against tampering and runtime code injections.
Core Features:
- Debugger State Polling: Hooks into Debug.isDebuggerConnected() and Debug.waitingForDebugger() to identify debugger attachments.
private fun isDebuggerAttached(): Boolean {
    return Debug.isDebuggerConnected() || Debug.waitingForDebugger()
}
TracerPid Surveillance: Implements /proc scans to extract TracerPid data, flagging tracing attempts.
private fun isDebuggerConnectedViaTracer(): Boolean {
    val tracerPid = File(ABC.getTracer()).readText()
        .lines()
        .firstOrNull { it.startsWith("TracerPid:") }
        ?.split(":")?.get(1)?.trim()?.toIntOrNull()

    return tracerPid != null && tracerPid > 0
}
Signature Validation: Cross-references APK signing certificates against a predefined whitelist, securing the app against repackaging.
private fun validateAppSignature(context: Context): Boolean {
    val validSignatures = ABC.sign().split(",")
    return packageInfo.signingInfo?.apkContentsSigners?.any { signature ->
        val md = MessageDigest.getInstance("SHA-256")
        val hash = Base64.encodeToString(md.digest(signature.toByteArray()), Base64.NO_WRAP)
        validSignatures.any { it.equals(hash, ignoreCase = true) }
    } ?: false
}
App Hard Kill: Executes a process kill upon breach detection to enforce immediate containment.
private fun handleVulnerabilityDetected() {
    android.os.Process.killProcess(android.os.Process.myPid())
    exitProcess(0)
}
3. Device Binding: Tethering Trust to Devices
Device binding anchors user authentication to a specific device by leveraging asymmetric cryptography, thus ensuring trust boundaries remain unbreachable.
Implementation Workflow:
- Key Pair Generation: Generates an RSA key pair using AndroidKeyStore for hardware-backed security.
val keyPairGenerator = KeyPairGenerator.getInstance(
    KeyProperties.KEY_ALGORITHM_RSA, "AndroidKeyStore"
)
keyPairGenerator.initialize(
    KeyGenParameterSpec.Builder(
        "device_key_alias",
        KeyProperties.PURPOSE_SIGN or KeyProperties.PURPOSE_VERIFY
    )
    .setDigests(KeyProperties.DIGEST_SHA256)
    .setSignaturePaddings(KeyProperties.SIGNATURE_PADDING_RSA_PKCS1)
    .build()
)
val keyPair = keyPairGenerator.generateKeyPair()
Server-Assisted Challenges: Implements a challenge-response mechanism for subsequent authentications, securing the handshake via private key signing.
val privateKey = keyStore.getKey("device_key_alias", null) as PrivateKey
val signature = Signature.getInstance("SHA256withRSA")
signature.initSign(privateKey)
signature.update(challenge.toByteArray(Charsets.UTF_8))
val signedChallenge = signature.sign()- Asymmetric Validation: Server-side validation confirms device authenticity, rejecting unauthenticated access attempts.
4. Code Obfuscation: Disguising Execution Paths
Obfuscation, a cornerstone of code-level security, masks application logic to stymie static and dynamic analysis.
Best Practices:
- Proguard Rules Optimization: Fine-tune rulesets to exclude critical APIs from reflection while obfuscating package names and sensitive classes.
- Dynamic Code Loading: Utilize dex encryption and dynamic module loading to obfuscate runtime behavior.
- Secure Configuration Storage: Leverage abstraction to prevent direct access to sensitive runtime configurations.
5\. Network Security Configuration: Mitigating Interception Risks
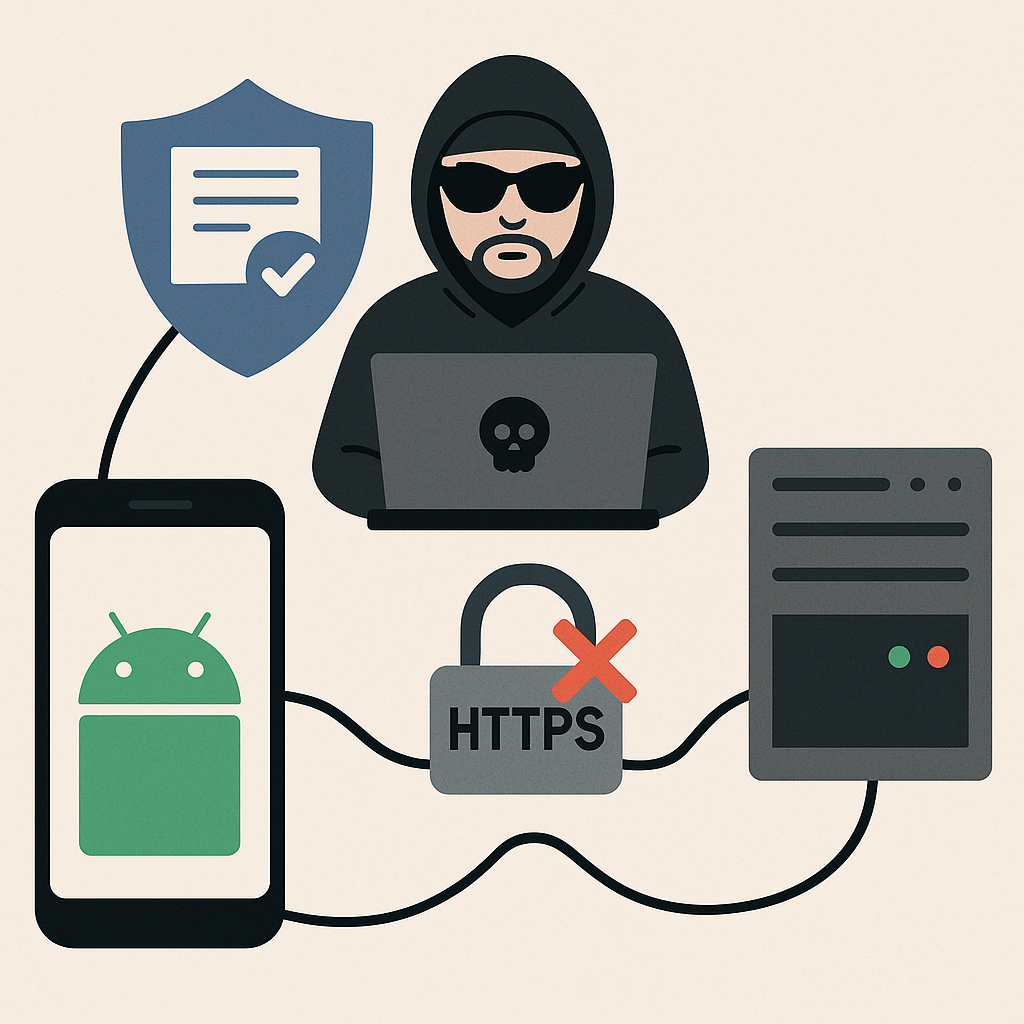
The Network Security Configuration file empowers developers to define and enforce app-specific network security policies declaratively through an XML resource. By configuring this file, apps can prevent untrusted network connections, disable cleartext traffic, and ensure strict adherence to secure communication protocols.
Key Benefits:
- Cleartext Traffic Protection: Blocks unencrypted HTTP traffic by default, ensuring that sensitive data is not exposed to man-in-the-middle (MITM) attacks.
- Custom Certificate Pinning: Allows pinning to specific CA certificates, mitigating risks from compromised Certificate Authorities or fake SSL certificates.
- Granular Control: Enables per-domain configurations for handling cleartext traffic, enforcing stronger policies for critical endpoints.
- Improved App Security Posture: Ensures compliance with industry standards like OWASP MASVS for secure communication.
Implementation: Define the network_security_config.xml in the res/xml directory to establish network policies.
<?xml version="1.0" encoding="utf-8"?>
<network-security-config>
    <!-- Default configuration for all domains -->
    <base-config cleartextTrafficPermitted="false" >
        <!-- Trust system certificates and enforce secure protocols -->
        <trust-anchors>
            <certificates src="system" />
        </trust-anchors>
    </base-config>

    <!-- Secure configuration for secure.example.com -->
    <domain-config cleartextTrafficPermitted="false">
        <domain includeSubdomains="true">secure.example.com</domain>
        <!-- TLS 1.3 is supported automatically on Android 9+ -->
        <trust-anchors>
            <certificates src="system" />
        </trust-anchors>
    </domain-config>

    <!-- Certificate pinning for api.example.com -->
    <domain-config cleartextTrafficPermitted="false">
        <domain includeSubdomains="true">api.example.com</domain>
        <pin-set expiration="2025-01-01">
            <!-- Replace with your actual SHA-256 certificate pin -->
            <pin digest="SHA-256">MIIBIjANB...</pin>
        </pin-set>
    </domain-config>
</network-security-config>
Register this configuration in the AndroidManifest.xml:
<application
    android:networkSecurityConfig="@xml/network_security_config"
    ... >
</application>
Conclusion
Security is not a product; it’s a continuous process. From root access detection to tamper-proof device binding, safeguarding your app against an array of evolving threats demands vigilance. Android developers can stay ahead of adversaries in this arms race by embracing abstractions, secure storage, and layered hardening techniques. Invest in proactive security — not as a reaction, but as a discipline.