Introduction
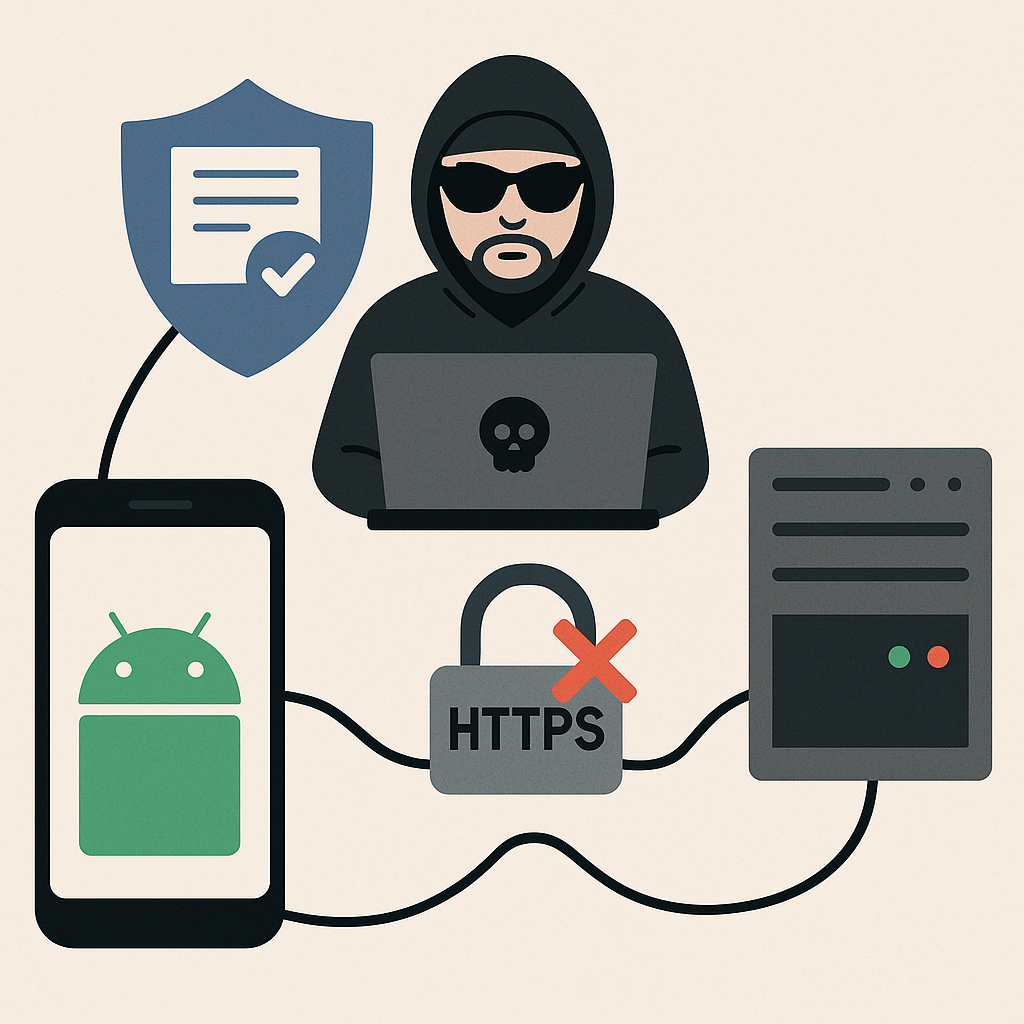
In the ever-evolving cybersecurity landscape, network security in Android apps is critical. Cyber threats like Man-in-the-Middle (MITM) attacks, rogue certificates, and compromised Certificate Authorities (CAs) can expose sensitive user data to attackers.
One of the most effective ways to counter these threats is through certificate pinning. But how do you implement it securely while ensuring that expired certificates don’t break your app? Let’s explore.
Why Should You Care About Certificate Pinning?
Most Android apps trust the default system’s Certificate Authorities (CAs), but here’s why that’s a problem:
- CAs Can Be Compromised — Attackers have exploited weak CAs in the past to issue fraudulent certificates.
- Users Can Be Tricked — If a user installs a malicious CA, an attacker could intercept their network traffic.
- MITM Attacks Are Getting Smarter — Traditional SSL/TLS security is no longer enough.
Certificate pinning ensures that your app only trusts a specific set of certificates, even if a rogue CA tries to intervene. Sounds great, right? But there’s a catch — you need to implement it correctly to avoid breaking your app when certificates expire.
How Do the Best Android Developers Handle Certificate Pinning?
Here’s what top Android security experts do when implementing certificate pinning:
✅ They Pin Public Keys, Not Entire Certificates
Certificates expire, but public keys remain stable. This approach ensures long-term security without unnecessary disruptions.
💡Hint: You can extract the SHA-256 hash of the certificate’s Subject Public Key Info (SPKI) and store it securely.
✅ They Plan for Key Rotation
A single pinned key is risky. Experts pin multiple keys — both the current key and a backup key — to handle certificate renewals smoothly.
💡 Hint: Use a secure mechanism to store and retrieve pinned keys dynamically.
✅ They Fail Securely
If the pinned certificate check fails, the app should immediately block the connection rather than falling back to the default system CAs.
💡Hint: Implement a custom X509TrustManager that rejects untrusted certificates.
override fun checkServerTrusted(chain: Array<out X509Certificate>?, authType: String?) {
    val spkiHash = chain?.first()?.publicKey?.encoded?.sha256Base64()
    if (!pinnedCertificates.contains(spkiHash)) {
        throw CertificateException("Untrusted certificate detected!")
    }
}
✅ They Keep Pins Updated
Regular updates ensure that new certificates are added before old ones expire, preventing unexpected outages.
✅ They Automate Certificate Updates (Background Updates)
Since certificates expire, your app should be able to update pinned certificates dynamically without user intervention.
💡 Hint: Use WorkManager with a Backoff Policy to check for certificate updates only when needed, ensuring minimal resource consumption.
💡 Hint: Ensure updates only trigger when necessary (e.g., certificates expire or are close to expiration). Avoid redundant network requests to reduce resource consumption.
💡 Hint: Introduce Provider-based architecture to fetch certificates from multiple sources (e.g., remote servers, local storage, or secure APIs) while keeping the implementation flexible.
💡 Hint: Implement a CertificateProvider interface that different providers can implement, allowing easy swapping between update mechanisms.
✅ They Use Secure Storage for Pinned Certificates
Pinned keys must be protected against reverse engineering and tampering.
How Does This Solution Ensure Maximum Security?
This approach to certificate pinning is not only robust but also resistant to common bypass techniques used during security testing. Unlike weaker implementations that attackers can manipulate using runtime hooks or SSL-unpinning frameworks, this method ensures:
- Strict enforcement of certificate validation — Only trusted certificates can establish a connection.
- No fallback to system CAs, making MITM attacks significantly harder.
- Prevention of dynamic analysis bypasses, securing API requests against interception.
- Enhanced security testing — By not allowing pinning bypass, security teams can thoroughly validate app defenses.
How This Approach Maximizes Security 🚀
This robust certificate pinning strategy ensures:
✔️ Strict enforcement of certificate validation → Only trusted certificates are accepted.
✔️ No fallback to system CAs → Eliminates a common MITM attack vector.
✔️ Tamper resistance → Protects against SSL unpinning attempts using runtime hooks.
✔️ Seamless updates → Automatically refreshes certificates before expiration, minimizing disruptions.
🚀 Ready to Secure Your Android App?
By following these best practices, you can ensure your app remains resilient against advanced security threats while maintaining a seamless user experience.
If you’re looking for a production-ready, tamper-resistant implementation, let’s connect! Let’s make security a priority, not an afterthought. 🔒🚀
📩 Reach out if you’re ready to fortify your Android app!
🔒 Stay Secure, Code Smart!